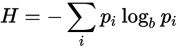Wednesday, January 17, 2018

Bitcoin Conspiracy - Who and Why? or when technology meets politics and economy


Yeah I know what you're thinking - "please, not another goddamn conspiracy theory", right? Well, I'll do my best to make this article as different and as logical as possible, although, it might be a little more political/economical than technical, but still informative.

OK, now almost everyone knows that at the end of 2017, one BTC cost almost 20,000 $ and that it was a very good investment years ago, but how did it all start and for what purpose?

Before I really begin, I would like to notice that all bitcoin transactions are publicly visible by everyone, thus bitcoin isn't an anonymous currency by nature, like Dash/Zcash for instance, as far as you don't publish your public key with your identity (like for donations).

The legend is that it was created by a Japanese as a decentralized cryptocurrency based on blockchain technology. I do believe that it could be done by a single man (as I reinvented blockchain in my time), but I don't really see the reason for staying anonymous, though some "big" projects creators preferred to hide (like Linux PaX), in this case it won't change anything since, the "Pandora's box" is already open and there is pretty much nothing the creator can do if something will go wrong (the community still has to accept some kind of "soft-fork", like it was with Ethereum or on altcoin with a larger block size (think Litecoin)).
For me this means only one thing - nobody suppose to know who made it and thus, the reason behind it.

So, who actually created it? You may hear different versions : cypherpunks, NSA, CIA, illuminati, lizards, aliens, you name it ...
I will go with a more-or-less realistic assumption, but in order to understand my statement, I have to mention a little bit of history.

What is currency nowadays? Just a paper that people believe is somehow valuable and represents a financial debt, like dollars. But before they were backed by real gold (taken from citizens), you could go to bank and say - "Here's thousand backs, now give me some real coins", the same was in Soviet Union, you could exchange rubles for a shiny metal, a paper was an equivalent for gold. But after a dozen years a man called Charles de Gaulle tried to do it for all the dollars in France, such exploit made USA lose much gold and then they (more precisely, Federal Reserve System, which not belongs to state) understood that it wasn't a very smart idea after-all. So, they just started printing papers, hoping that people will still believe that they are valuable, and later with IT, they just simply making zeroes and ones, without any "material base" what-so-ever. Backing dollars with gold as intrinsic value was an attempt to universalize it and force everyone to use it by USA, which became the richest country with the largest gold reserve just after the WWII.


A currency is itself a debt, but do you know how much USA owns? Very, very much, more than there are resources in the whole world, which will eventually lead to its inevitable economical collapse and America won't ever be "great again", while printing all these bucks. So, as time passes, country has to get rid-of all this debt, a war isn't a bad solution as debt burning (I should mention Ukraine ... maybe later), but after the financial crisis, a solution should be found quickly. Yet, what if we made a new currency related to dollar as its alternative and force everyone to use it instead while keeping a big part of it? Eureka! Total control. Surely, we will have to give the blockchain technology as well, but that's an acceptable price.

OK, enough politics for now, let's go technical, let's speak about hacking, although malware creation isn't really hacking, but still related to the topic.
Some malware researchers/analysts have found some links between some ransomware attacks and government hackers (specifically Equation Group (NSA-TAO)), I may even speculate that some of their tools were leaked on purpose as a justification/endorsement for such attacks (like, maybe, 9/11?), or that a state should actually arrest someone who stopped such attack, or that stocks are hacked not just by criminals and finally, that "anonymous black-markets" are actually law enforcement honey-pots. Not even mentioning a strange recursive hash theft/backdoor discovered recently. Also, Crypto Dip in the middle of January 2018 by "banning" cryptocurrencies, has cut their prices almost ten times for some cases, but in some "particular" cases, the price raised a lot and, where truly Silk-Road seized bitcoins went? So many questions, yet such uncertainty.

An alternative version is that it's just another pyramid that spiked-up after a financial crysis, like it was in USSR in case of MMM, but in this case, it's going to be worldwide and there is no one to put to jail for it. You might ask however, how such scheme could even work? Well, it's pretty good illustrated in a book called Dunno on the Moon with "The Society of Giant Plants" as example, but to put it in the nut shell, let's say that a company which costs 100 thousand dollars sells its 100 shares, that would mean that each share cost one thousand dollars, and the price varies regarding multiple criteria, such as being successful or not. The thing is that if people will buy the shares, they will become less and less available and since people want more and more, the shares will raise in price because, demand creates offer. On the other hand, if suddenly the price will go down for whatever reason and if everyone decides to sell back the shares, while nobody wants to buy it, the shares will cost almost nothing and drop in price even lower. And it works, because of such psychological phenomenon as greediness, which is the base for almost any pyramid (and probably the only intrinsic value of cryptocurrencies), especially if it's heaped by media (like YouTube).
After-all, currency is indeed currency when you can buy something with it or exchange for green American presidents of Colon... I mean Columbus country. Finally, even if it's a non-state-sponsored pyramid, the state itself doesn't seems to be worrying about a potential dollar concurrency too much, it only tries to profit from it.


That was probably pretty simplified, yet pretty clear, but how bitcoin price is determined since, it's not material-based and when did the first stock exchange begun to accept it? If I'm not wrong, its wide recognition and acceptance begun in 2013, the same year when the gold price went tremendously down for the first time in history, coincidence?

Now, let's take another powerful state - Russia. They want to make their own cryptocurrency, some kind of cryptoruble. For me the reason is pretty obvious - total control. If the blockchain technology will be state-centralized and the only authorized, which Russia wants, the state will control all the economical flow in the country, every payment of everyone.
The justification for such maneuver is not only to "fight terrorism" cliché, but to fight corruption for example, so the intent may seem to be good. However, one should realize that he/she/it would have practically no privacy of market since, everything what goes from and to his/her/its account is state-monitored. Money is power, and Russia will take it from its citizens sooner or later, just like Soviet Union took private property. Suppression of private property is an attribute of Socialism ("from each one an ability, to each one a work"), which is a transitional step from Capitalism to Communism, history repeats itself ... by spiral (according to Marx at least).
Will it be good or bad? I'm not predicting anything, but I just worry about the vectors Russia's heading (and hope that it will not take an example of Estonia's digitalization mistakes). Considering the CIS summit of december 2017, that was probably a subtle proposition to create a common economical space, thus one could predict a Union of Crypto Socialist Republics - UCSR :) and... another cold war phase, subtly declared by Atlantic Council report.

Do I have bitcoins at the moment? No, and I discourage everyone to buy and use them not only for political, but also for philosophical reasons.
A currency is not a merchandise that can be traded on stock, you suppose to buy things with money, but not to buy money with another money, it contradicts the currency intent and creates problems, bitcoin isn't an exception, so please stop being greedy and financing economical slavery along with capitalistic pyramid.

"But hey! It's just a theory! A conspiracy theory! Thanks for reading!"

P.S. soon I might make a proposition of a new economical model based on cryptography and sociology.


Wednesday, December 13, 2017

SkyrimCrypt - Deniable Encryption and Steganography in Computer Games


Even if TES V Skyrim was released more than 6 years ago, people still play it, people still like it and I found a very interesting and nontrivial way to use it as a decoy to hide information, basically transforming it into a steganographic crypto-container (like TrueCrypt).

You might know from news about MMORPGs espionage, however, this is becoming more than real elsewhere ... I thought that only USA "seek terrorist" in order to do what they want, but it's not a political article.
Perhaps you could use online games in order to have a private chat, it's not a bad idea on a perspective of a decoy, but in a point of security view, there is no encryption and plenty of logs, so if you're going to be under suspicon, it's not going to be private anymore. Nonetheless, how to use offline games as a secure storage? This is what my article is about.

You might wonder - there are already solutions, why bother with another-one? Well, the reason is that I don't agree with the existent. Crypto-containers like TrueCrypt/VeraCrypt/LUKS can be identified and even if you will remove the header (thus adding deniability) you might think that nobody would think that it's an encrypted data, unless you know some mathematics behind cryptology. You see, encrypted data is "random" by nature, a more precise term would be - entropic, and entropy can be calculated, meaning that if you have a huge entropic file (containing "random" data), that would raise a suspicion that may be followed by brute-force that may be followed by cryptanalysis that may be followed by torture. Probably I'm exaggerating for today, but perhaps tomorrow it will be the case.

Anyway, the article suppose to be about games and not about paranoia, so let's do some tests with Skyrim. I have one installed on my Linux with Wine, works not so great, but works. But, do you know what's special about Skryim? Mods, plenty of mods exist for it and if you play Skyrim you probably have dozens of them, but not everybody develop mods, those who do, know their structure, fragmentation and extensions, specifically BSA. Now, let's look at them in the Skyrim's Data folder:

 
Those are classical Skyrim "mods", which may be included right after the purchase (for some editions). BSA is basically a compressed archive, thus "random" by nature, although it has a deterministic header, it can have a very big size too.
Now, let's look at one of them:


I specifically chose the one with textures because, mathematics. So, let me explain you all this. As ent tool shows, 7.97 out of 8 bits in file looks random, which is 99.7% of them, plus it indicates that the file was indeed well compressed, the chi-squared distribution isn't good though. It also showed some more interesting statistics, but they are less important and I'll have to explain what I already said, to begin, here's the file's bytes distribution:


As you can see, it's not so random as the entropy may show us, but how is that calculated after all? Well, when dealing with IT we often will reference to Shannon's entropy, which indicates how "random" are bytes of a file:


Basically, you would  perform a negative sum of probability occurred for each byte by multiplying it by the logarithm (necessary power) in base two of itself.
Encrypted file is 8/8 entropic (which is sometimes more than a randomly generated file), just like a ZIP archive and it's chi-squared distribution is about 290 for 95% to be sure, now about that:


Basically, it's the fraction of the square of the difference between the estimated distribution and the observed one to the estimated distribution.
That is very interesting because, it shows us if there is a big difference between what we observe and what we estimate, that our hypothesis is true with a certain probability. And here is where I'm not really agree with the ent tool because, it doesn't really shows the probability of being certain (50% in the best case according to them), but let's just say that the lower this number is, the more you can be sure that the data are "really random" and as you can see from the screenshot, 67 million is way bigger than few hundreds, thus we will reject the random nature of such distribution.
I know that you still may have some questions about all this, so feel free to make some web searches in order to fully understand such useful math.
That was to say that even if our file is entropic, it may not be randomly distributed.

Besides, as you may notice the content of the header isn't that random, but it begins from a couple thousands bytes:


So, we can copy the first non-random bytes and then append out crypto-container to it, claiming that it's just a mod for Skyrim whereas it's not, and to extract, we just specify the offset for dd (or directly) and decrypt :


Nevertheless, mathematics will show the truth behind such decoy, as you can see even if adding thousands of nonrandom bytes to 500Mb that wouldn't affect the entropy, neither the chi square, thus raising the suspicion for that file and uncovering it.
But, I'll assume that it would be enough in the near future to bypass border controls in some countries.

Of course, it will be preferably to have a whole steganographic OS or a disk, but don't worry, R&D in progress :)

By the way, if you're afraid that somebody someday might decrypt your files, instead of encrypting them, just try to decrypt :) that way you will have to encrypt the files in order to receive their original form (with the last block lost however) :


You might ask me why I didn't publish a tool to make such BSA mods? I won't and discourage everyone to do so for the same reason this article is written - stealthing. The existence of that tool may also make you suspicious and if you have logs of using it, it's game over. The point is to have no trace whatsoever. If you want more details about what I just wrote, you can checkout one of my works.

Finally, even if you're not going to use my technique, I still hope that you learned something interesting and perhaps useful from my article.
That said, let's make Skyrim sneaking "great again" :)


Friday, September 22, 2017

WiFi danger demystified - scientific truth and practical solution


 Is WiFi dangerous?
 You can find so much information about how cancerous it is, but on my opinion, it's far to be logical and structurally substantiated and, almost no one proposes a practical solution.
In this article I'll try to simply explain the nature of radio-telecommunication using science and propose simple, but effective solutions.

First of all, what is WiFi? Many of you know that it's radio waves, thus electromagnetic emissions, which are caused by the induction phenomenon, transforming electronic current (electrons flow) into radio waves (electricity is tightly linked to magnetism) and vice-versa. Some of you might even know one of the most common frequencies of such radiation - 2.4 GHz (two billion four hundred million cycles per second), however, fewer knows about the frequency of the microwaves ovens, which is almost the same - 2.45 GHz.

 Let's deal with the microwave at first, why exactly this frequency? You see, the point of the microwave is to make food hot, especially water, and the frequency of its optimal dielectrical heat is exactly 2.45 GHz. Water molecules are polar matters, this means that they have an electrical charge (+ and -) from which depends their position in space, thus, producing a particular electromagnetic radiation will change their charge, molecules will move (change orientation) and from frequency (and wavelength) will depend their speed, and a fast molecule is a hot molecule. In brief, and omitting chemistry and physics details, that's how a microwave oven works.


Now about the WiFi. Why routers, designed for communication, use almost the same frequency that the microwave in the kitchen? Unfortunately, the science won't help much here, except maybe psychology because, the reason lies in legislation (and not conspiracy theory). The thing is that all the radio spectrum, as well as the ground, belongs to the state (government), and nobody has right for any radio emission without an authorization, this is one of the reasons for a quit height cost of mobile communication because, operators rent certain spectrum from the state. Nevertheless, there are frequencies (ISM band) that do not require an authorization and their usage isn't heavily restricted, besides, the antenna can be a simple wire (omnidirectional) with the length of 12.5 cm or 6.25 or even 3.125 (factor of the wavelength). Unfortunately, as history shows, legislation is more pointed towards business, rather than technology and health, especially in the USA, where many standards are adopted.

Turns out that we are all radiated by the microwave, and for the health this is not good since, we are practically boiling out brains ... For that reason, the WiFi signal is less strong while raining or in the forest (vegetation), because water absorbs a part of it. Nonetheless, the reality isn't so terrifying. The signal's power is limited and very far from the microwave's, without even counting the obstacles, the harm is pretty insignificant, but still is (like if there are 50 hot-spots and you're sensitive to EMF).

So, what to do? Change the standard? Wear foil hat? Disable WiFi? Once again, I'll try to propose a realistic solution. Everything is simple: switch the wireless router to 5 GHz frequency, this will not only reduce the harm greatly, but improve the speed as well, even if the distance will be at cost. And please, don't buy any kind of "100% EMF-proof protection talisman", at least if it's not a Faraday cage, as I have already proved, it's a scam. I mean there were some phone shielding, but modern smartphones aren't so radiating at all (by them self, see below for the network).


PC is, however, much more dangerous than a phone, but at a certain distance, waves lose their power and, well, such distance if fully provided by a chair, according to my measurements it's just few tens of centimeters, especially if you use ergonomics to your advance.
But even if you managed somehow to completely shield a PC, you should also do something with cables, like headphones because, they are quite powerful actually and since very close to the head, aren't completely safe, though it isn't still enough for a meaningfull damage.
Ethernet cable (aka RJ45) on the other hand is already shielded in many cases because, network engineers have figured out that by twisting pairs and putting foil will reduce the EMF and so the transmission corruption.


Anyway, don't forget that WiFi isn't the only one working in 2.4 GHz spectrum, Bluetooth for instance, also use it, and a microwave under the ear won't do any good (wireless headset), if of course isn't worn all day long, besides the strength (power) of Bluetooth (especially 4LE) is very weak, thus less harmful.
GSM/GPRS/3G/4G/5G work in different spectrum, although not so far from the microwave, the power is much more higher, as well as the potential harm (while speaking long time), so I'll advice to switch to 5G (12-60 GHz), after it will have at least some security and the operators will implement SDR.

Hope that this article was usefull to you and everyone else in the radius of several tens of meters.
Unless, you already have a "Faraday suit" :)


Tuesday, August 15, 2017

Practical WiFi hosts triangulation with Kismet, Python and Gimp for de-anonimization


NOTE - I created an independent project in order to automize some math

In this article, I'll try to explain how to (approximately) locate and identify any host on any WiFi hotspot, encrypted or not (link layer frames), using triangulation and some tools.

The purpose is to find an anonymous user who spoofed his MAC and consumes all the bandwidth by downloading Game of Thrones.

The exact mathematical therm is Trilateration actually.

So, let's say that we have a typical setup:


Many devices are connected to a single router, in fact, it also can be done with multiple bridges.

Our task is to estimate the location of a precise host (not only the router it-self), in order we can map it.

For now, we need to see the MAC addresses connected to specific AP (access point) and their RSSI in dBm (Received signal strength indication in decibel-milliWatts).

For that we can use WiFiChannelMonitor for Windows or (in our case) Kismet. One can try AirCrack-NG as well, but there are some tricks to add, like frequency channels, ACK/CTS/RTS frames and BSSID associations.

Just after launching Kismet, you should see a prompt for server starting, just press Tab (for navigation) and Enter (to select) Yes :


Name it like you want and Start :


Then, you will have to specify your network interface for promiscuous mode :


Just select your WiFi card or an already monitored interface (like mon0) :


Finally, just close the Console Window :


Now, you should have a pseudo-gui interface :


So, let's find a WiFi hotspot, by applying ESSID filtering (pressing Esc) and navigating using arrow keys :


Then just select (without Enter) the hotspot and you will see all the clients (MACs) connected to the network.
If you select it (Enter), you will see more details (I'm using 5GHz WiFi and not 2.4GHz like most of you) :


OK, let's see the details for the clients (by pressing Esc) :


Lastly, we will need to see their electromagnetic emission power (signal) level (basically, a decibel (power ration) for milliWatt (electricity consumption)), which is not displayed by default :


Now, we are ready :


Kismet will also show the manufacturer (based on MAC vendor) and you can sort them if you want.
Note that even if you return to main window, you will still see the power level :


OK, as you can see Kismet measured the power of my router (67 dBm) and of my smartphone (30), I'm using cable for my PC, so it's not displayed.
Based on such values, we can estimate the distance, but it will be better if we could calculate an approximation, what I did :


You just have to specify the AP frequency (displayed by Kismet as well) in MHz and the host power level (dBm).
The source code of the script can be found on my GitHub.
The formula that I used isn't the most precise (especially if you would make tests with different frequencies), but it's sufficent for our practical purpose.You can also, calculate logarithm with bc by the way, but I know that some of you are using Windows and not big fans of Cygwin, so I decided to make it as portable as possible, thus writing the code in Python.

So, now we know the distance, my smartphone is on my right (15 cm), so it's pretty easy to locate it in this case, but what about the router (10m)? Here's where triangulation (or trilateration) comes in place.

I'll use Gimp as a graphical editor, but you're free to use what you're more comfortable with (PhotoShop, Paint, etc).
So, let's make a square image of 500x500 pixels, which will correspond to 50x50 meters :


And make a circle with radius of 100 (10 meters), thus a diameter of 200, which is equivalent for a flat (not circle) surface of 200x200 (20 meters), or you can just enter 100x100 for simplification :


Just for better comprehension for the next part, let's color it as well :


Alright, we are at the center of the circle (my room), and the host can be anywhere on the end of the circle.
So, let's move like 5 meters backward (half of the radius) and measure the distance again.
From my kitchen, it will be 6.5 meters, so let's trace one more circle :


Now we can be sure that the host is located either few meters left, either few meters right.
If we decided to step forward or to the side, the distance will increase, but we will still have the two points of intersection.
So, let's make the final 3rd measurement stepping backward again and right few meters to my guest room, and measure 3.3 meters :


If we decided to step left, the distance would increase once again, but we will still have our unique intersection point (I just don't have that much place in my apartment).
OK, now we know almost the exact position, which was right lower corner from the beginning (my room) :

That's it for my router and since, Kismet will now display the power level of all clients, you can do the same for any connected host.
As you can see, it's quite simple and can be automize, but not easy to develop at large scales considering different antennas, obstacles, etc

I hope that you have learned something about WiFi, physics, radio and math.
Now if someone would say "it's anonymous to spoof MAC and connect to WiFI", you should have a smile and remember my article.